 UAE, UNFILTERED
Sharjah Police Says Four Linked Cybercrime Networks Moved Billions Through Digital Wallets
Sharjah Police says four connected international cybercrime networks used hacking, wallet theft, extortion, fraud, data trafficking and virtual assets in one cross-border operation. The structure matters more than…
The case shows organised cybercrime operating as a connected service stack, with hacking, stolen data, social engineering, wallet theft and money laundering divided across specialist groups.
UAE businesses, security teams, digital-asset users, financial institutions and residents targeted by phishing, account takeover or wallet theft.
The AED65 billion figure refers to company assets police say were protected, not stolen funds. Public reporting does not identify every affected entity or victim.
Investigators will continue tracing digital wallets, financial flows, devices and international links while institutions strengthen cross-border intelligence sharing.
Protect identity, email and wallet access together. Use strong authentication, verify unusual requests independently and preserve transaction details if fraud occurs.
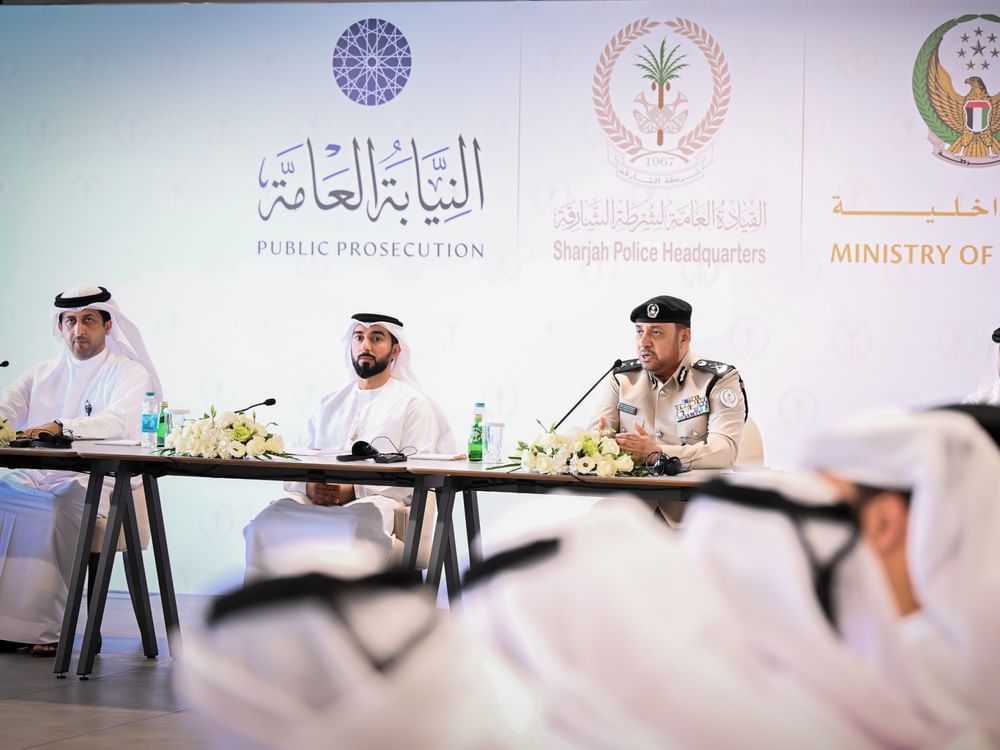
Sharjah Police says it has dismantled four interconnected international cybercrime networks in an operation involving 33 suspects from 12 nationalities.
The arrest count is significant.
The more important detail is how many criminal functions were operating together.
Police say the networks were involved in cyber intrusion, money laundering through virtual assets, digital-wallet theft, fraud, extortion, trafficking in compromised data and violent assault.
This is not a single scam campaign.
It is closer to a criminal services stack.
The operation was about infrastructure, not one fraud script
Sharjah Police named the operation “End of Battle”.
According to the force, investigators identified four linked networks and pursued principal suspects across borders with support from the Ministry of Interior and international partners.
Police say the investigation helped protect more than 30 companies and institutions worldwide with assets valued above AED65 billion.
More than AED200 million was confiscated, and more than 3,000 digital wallets were subjected to examination and verification.
Police also said the wallets had recorded financial movements worth billions.
The AED65 billion figure is protected asset value, not stolen money
This distinction matters.
The AED65 billion figure refers to the value of company assets police say were protected from potential harm.
It is not a confirmed fraud-loss figure.
The amount confiscated was reported separately at more than AED200 million.
Those figures should not be combined or described as money stolen from victims.
Why connected criminal functions matter
Modern cybercrime increasingly separates tasks.
One group may steal credentials.
Another may sell compromised data.
Another may drain wallets.
Another may convert stolen value through virtual assets.
Another may recruit money mules or intimidate participants.
When those functions connect, investigators are no longer chasing one scammer and one victim. They are tracing a supply chain.
Robius has been seeing the same pattern from the victim side
Our 2026 UAE scam-pattern roundup showed how different fraud campaigns reuse the same building blocks: impersonation, credential theft, urgency, remote access and payment redirection.
The recent government-bill discount scam exposed another layer. Stolen cards, compromised identities, legitimate payment portals and cash-out channels can all sit inside one fraud chain.
The Sharjah Police case shows what that ecosystem looks like from the enforcement side when multiple specialist functions are tied together.
Digital wallets are useful to criminals, but they are not invisible
Virtual assets can move quickly across borders and through large numbers of addresses.
That can make tracing difficult.
It does not make the flows anonymous by default.
Public blockchains can preserve transaction histories, while exchanges and service providers may hold account, device and identity records.
The hard part is connecting blockchain activity to people, infrastructure and offences across jurisdictions.
The police statement’s reference to more than 3,000 wallets under review shows how large that mapping exercise can become.
AI appears in the criminal toolkit too
Sharjah Police says the networks used artificial intelligence in carrying out criminal activity.
The public statement does not specify which AI tools or attack stages were involved.
That means it would be premature to describe the case as an “AI cyberattack”.
AI may have been used for social engineering, automation, targeting, content generation or other support functions.
We do not yet have enough public detail to say which.
Deepfakes and data trafficking belong to the same trust problem
Robius recently examined Dubai Police’s warning that deepfakes can make genuine evidence easier to deny.
Trafficked identity data creates a related problem.
Once criminals have names, phone numbers, account information, documents or authentication details, impersonation becomes more convincing and account recovery becomes harder.
The attack is no longer only technical.
It becomes a trust attack across banking, telecom, government and personal communication.
Cross-border recovery is often the hardest part
Cybercrime can be planned in one country, executed from another, monetised through a third and harm victims somewhere else entirely.
Sharjah Police says principal suspects were arrested and recovered from abroad.
That is important because attribution without jurisdictional cooperation often leaves enforcement stuck at the identification stage.
The case highlights why cybercrime response increasingly depends on information sharing, extradition or transfer processes, financial intelligence and coordination with digital-asset service providers.
What businesses should take from this case
The practical lesson is not “crypto is dangerous”.
It is that criminal groups combine digital and human weaknesses.
Businesses should assume an attacker may move across multiple layers:
- employee credentials;
- email accounts;
- cloud services;
- customer data;
- payment systems;
- digital wallets;
- social-engineering channels.
Controls need to connect those layers too.
The Robius Read
The Sharjah operation is significant because it shows cybercrime behaving like an organised business network.
Hacking, stolen data, wallet theft, fraud, extortion and laundering are not separate headlines when the same ecosystem can move victims from one stage to the next.
For defenders, that means stopping one phishing page or freezing one wallet is useful but incomplete.
The stronger response follows the full chain: access, identity, infrastructure, money movement and the people coordinating it.
Sources
- Sharjah Police: End of Battle cybercrime operation, 15 October 2026
- Emirates News Agency: Sharjah Police cybercrime operation, 15 October 2026
Checked 16 October 2026. The AED65 billion figure refers to assets police say were protected, not confirmed stolen funds. More than AED200 million was reported confiscated separately.
Robius.news | Dubai, UAE | 2026 | Built to be first. Built to be trusted.