 UAE, UNFILTERED
The UAE Says Every Government AI Agent Must Plug Into a Control Tower. That Changes the Governance Question
The UAE says every deployed government AI agent must connect to an Agent Control Tower, with actions and reasoning logged and audited by both agents and humans. The…
The UAE has disclosed a technical supervision layer for government AI agents, suggesting governance is being built into runtime infrastructure rather than left only to policy.
Government technology teams, AI vendors, public-sector leaders, enterprise buyers and residents affected by automated government actions.
The public disclosure does not yet define technical scope, retention, telemetry, blocking rules or which federal and local agents are connected.
Watch for technical standards, deployment scope, permission models, incident-handling rules and evidence that the control tower can prevent or reverse harmful actions.
When evaluating agentic AI, ask who owns the action, what gets logged, what can be reversed and which decisions remain outside agent authority.
The UAE has disclosed one of the clearest pieces of its agentic AI governance architecture so far.
Every deployed government AI agent must plug into an Agent Control Tower.
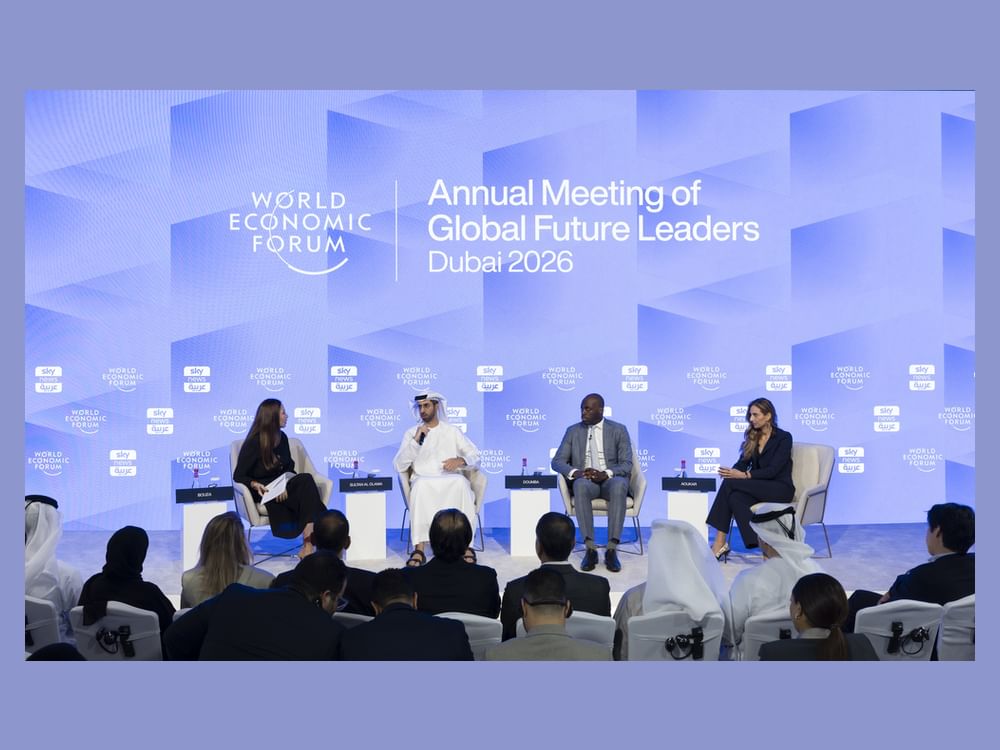
Omar Sultan Al Olama, Minister of State for Artificial Intelligence, said every action and “thought” is logged, with audits performed by both agents and humans.
That is more concrete than another commitment to “responsible AI”.
It suggests the UAE is trying to govern autonomous systems at runtime, not only through policy documents written before deployment.
A policy can say what an agent should do. A control tower can see what it actually does
Traditional AI governance usually focuses on approval before launch: model selection, risk assessment, data rules and human oversight.
Agentic systems create another problem.
Once an agent can take actions, call tools, access systems or execute workflows, governance has to continue after deployment.
A central control layer can potentially answer questions that static policy cannot:
- Which agent acted?
- Which system did it access?
- What action did it attempt?
- What data informed the action?
- Was the action approved, blocked or reversed?
- Which human or entity remains accountable?
The UAE has also drawn a red line around human livelihood
Al Olama said the government is not allowing AI agents to make decisions that affect human life or livelihood where the risk of error exceeds its tolerance.
Low-risk administrative tasks such as passport renewal may be suitable for greater automation.
Higher-impact decisions require a different threshold.
This distinction is important because “agentic government” can sound as though every service is moving toward full autonomy.
The public description suggests the opposite. The UAE is trying to define which classes of action can be delegated and which must remain under stronger human control.
This is the architecture behind the AI-native government story
Robius has been tracking Abu Dhabi’s push toward AI-native government by 2027.
That ambition becomes more credible when the governance layer is technical rather than rhetorical.
Training programmes such as AiNative build workforce capability. Platforms such as TAMM are moving toward more proactive service delivery. The Agent Control Tower is a different layer: it is about supervising what autonomous systems do after they have been given permission to act.
Logging “thoughts” needs a precise definition
The phrase is striking, but it should not be overinterpreted.
Public reporting says agent actions and “thoughts” are logged.
That does not tell us exactly which internal traces are retained, how long they are stored, whether they include model reasoning summaries, tool calls, prompts, intermediate outputs or policy checks.
Those details matter.
A useful audit trail should preserve enough information to reconstruct why an agent acted without creating unnecessary privacy, security or data-retention risk.
Human audit and agent audit solve different problems
Automated auditing can monitor scale.
Another agent can flag unusual behaviour, policy violations, abnormal tool use or actions outside expected patterns faster than a human team can review every transaction.
Human review provides something different: judgement, context and accountability.
That combination is more credible than relying entirely on either layer.
But it creates a new question: who audits the auditing agents?
The control tower itself becomes critical infrastructure.
Reversibility may be the most important design requirement
At the same WEF session, speakers emphasised permission levels and the ability to reverse harmful actions.
That is a useful way to evaluate government agents.
A recommendation is one thing.
An action that changes a record, sends money, denies a service or affects a citizen is another.
The higher the impact, the more important it becomes to design for:
- explicit permission boundaries;
- human approval points;
- rollback mechanisms;
- clear escalation routes;
- tamper-resistant logs.
TACTICA shows why this matters beyond public services
Robius recently examined TACTICA’s use of agentic AI for decision intelligence.
The same governance principle applies there.
The closer AI moves to operational or high-consequence decisions, the less acceptable it becomes to say simply that “the model recommended it”.
Decision systems need inspectable data lineage, permission boundaries and a clear human owner.
What we still do not know about the Agent Control Tower
The public disclosure leaves important architecture questions unanswered.
There is no detailed public technical specification showing:
- which government agents are already connected;
- whether the control tower applies across federal and local government or only defined deployments;
- what telemetry every agent must send;
- how policy rules are enforced in real time;
- how incidents are escalated;
- how long audit records are retained;
- which actions can be automatically blocked.
Those are the next details worth watching.
The Robius Read
The most important part of the UAE’s agentic AI story may not be the agents.
It may be the system watching them.
If every government agent has to connect to a shared supervision layer, the UAE is treating agent governance as infrastructure rather than paperwork.
The next test is whether that infrastructure can do more than log activity after the fact.
The stronger model would detect risky behaviour, enforce permissions, preserve auditability and make harmful actions reversible before a citizen feels the consequence.
Sources
- Emirates News Agency: UAE discloses Agent Control Tower for deployed AI agents, 14 October 2026
- Khaleej Times: UAE red line on AI decisions affecting livelihood, 14 October 2026
Checked 16 October 2026. The UAE has publicly described the Agent Control Tower and audit model, but detailed technical architecture and deployment scope have not been published.
Robius.news | Dubai, UAE | 2026 | Built to be first. Built to be trusted.