 UAE, UNFILTERED
Your Staff Are Already Using ChatGPT. A UAE SME Needs an AI-Use Policy Before It Needs Another Tool
Employees are already bringing ChatGPT, Claude and Gemini into everyday work. For UAE SMEs, the immediate problem is not whether to adopt AI. It is deciding what staff…
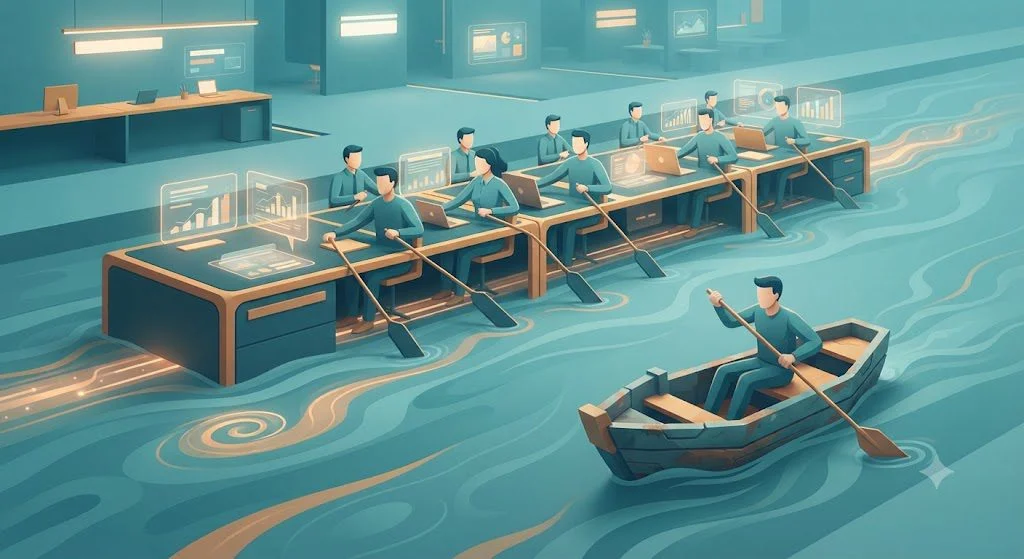
AI adoption often starts through employees before a company has chosen tools, accounts, data rules or approval processes.
UAE SME owners, operations managers, HR teams, IT leads and anyone responsible for customer, financial or confidential business data.
Business-grade AI controls reduce some risks but do not prevent employees from uploading the wrong data, connecting broad sources or trusting incorrect outputs.
As AI tools connect to email, drives, CRM and workflows, SMEs will need to move from prompt rules toward access, integration and agent-governance controls.
Audit which tools staff already use, define prohibited data, approve specific accounts and tools, and require human approval for high-impact actions.
Your company may not have bought an AI platform.
Your employees may already be using one.
They are drafting emails in ChatGPT, summarising PDFs in Claude, asking Gemini to rewrite client documents, using AI meeting tools and pasting spreadsheet data into assistants because it saves time.
That gap between official company systems and employee-selected AI tools is often called shadow AI.
For a UAE SME, the first governance problem is therefore not “Which AI should we buy?”
It is “What are people already doing with company information?”
Shadow AI is not the same as malicious behaviour
Most employees who use an outside AI tool are not trying to leak data.
They are trying to finish work faster.
That is why a policy built entirely around prohibition usually misses the problem. If a useful tool is blocked without an alternative, staff may simply use a personal account or another service outside company visibility.
The better starting point is to separate low-risk use from sensitive use.
The first risk is what employees paste into the prompt
A harmless request might be: “Rewrite this generic sales email.”
A very different request is: “Summarise this customer complaint,” followed by a full name, phone number, account history and order details.
The same interface can move from low-risk productivity to sensitive-data handling in one paste.
That is why companies need rules around information classes rather than vague instructions to “use AI responsibly.”
Consumer and business AI products are not automatically the same data environment
This is one of the most important distinctions for employers.
OpenAI states that content from its business offerings, including ChatGPT Business, Enterprise and API products, is not used to train its models by default. Business products also provide organisation-level security and administrative controls.
Consumer services have different settings and controls.
Anthropic similarly gives organisations management controls for Claude for Work plans that are different from individual consumer accounts.
The point is not that one vendor is “safe” and another is not. The point is that the account type, contract, retention settings, integrations and admin controls matter.
A UAE SME policy can start with five rules
1. Define what employees must never paste into unapproved AI tools
Examples can include customer identity documents, bank information, passwords, API keys, payroll data, confidential contracts, unpublished financial information and sensitive HR records.
The list should reflect the company’s actual work. A furniture retailer, broker, clinic and software company do not handle the same risk.
2. Name the tools employees are allowed to use
Do not make staff guess.
Approve a small set of tools for defined purposes and explain which account type must be used.
If the company already relies on Microsoft 365, for example, the governance decision may be different from a business using standalone consumer accounts. Robius’s Microsoft 365 Copilot review looks at how the product is increasingly becoming an AI work surface rather than just another Office app.
3. Separate assistance from autonomous action
Using AI to draft a response is not the same as allowing an agent to send the response, approve a refund, modify a customer record or execute a financial workflow.
The closer AI moves to action, the more explicit the approval and audit rules should become.
This is especially relevant as Dubai pushes companies toward agentic AI. Our analysis of Dubai’s plan to train 14,000 companies in agentic AI argued that training is easier than redesigning workflows and accountability.
4. Decide who reviews new AI tools
A 30-person company does not need an AI ethics committee.
It does need an owner.
That may be the operations manager, IT lead, information-security contact or a small approval group. Someone should know which tools are in use, what data they receive and whether they connect to company systems.
5. Give employees a safe way to ask
If the policy only says “do not,” staff will work around it.
Create a simple route for questions such as:
- Can I upload this PDF?
- Can I connect this AI tool to Google Drive?
- Can I use an AI transcription service for this meeting?
- Can I paste customer data if I remove the name?
- Can this agent send messages automatically?
Good governance reduces guessing.
The second risk is connected apps
Modern AI products increasingly connect to email, calendars, cloud drives, code repositories, CRM systems and other company tools.
That changes the risk profile.
A prompt may expose one document. A connected integration may expose an entire class of documents if permissions are too broad.
SMEs should review connectors and integrations as carefully as they review the AI model itself.
The third risk is that AI-generated work looks finished before it is verified
Data leakage gets most of the attention, but quality control is just as practical.
An employee can produce a polished legal explanation, customer response, quotation or analysis that is wrong.
The output may look more confident than the employee’s own draft, which makes errors harder to spot.
A useful policy should therefore define which outputs require human verification before they leave the company.
What should always stay human-approved
The answer depends on the business, but common examples include:
- contracts and legal commitments;
- financial transfers and payment instructions;
- employment decisions;
- customer compensation;
- regulatory submissions;
- security changes;
- public claims presented as company facts.
Do not confuse “not used for training” with “nothing can go wrong”
Business-grade AI protections matter, but they do not replace internal governance.
An employee can still upload the wrong file, share a generated link, connect an overly broad data source or accept an incorrect output.
The vendor handles part of the risk. The company still owns the workflow.
A practical 30-minute SME audit
Before buying another AI subscription, ask five people in different roles:
- Which AI tools do you use for work?
- What do you paste or upload?
- Which company systems are connected?
- What outputs do you use without checking?
- What task would you automate tomorrow if you were allowed?
The answers will tell you more about your actual AI risk than a generic policy downloaded from the internet.
The Robius Read
Most UAE SMEs do not need a 40-page AI policy.
They need a clear operating rulebook that matches what employees are already doing.
Start with the data. Decide what can leave the company environment. Name approved tools. Separate drafting from autonomous action. Put a human approval point around high-impact decisions.
Then expand the policy as the workflows become more capable.
The worst time to discover your company has a shadow-AI problem is after a customer document, confidential contract or internal dataset has already been uploaded somewhere nobody was monitoring.
Sources
- The National: shadow AI risks for UAE employers
- OpenAI: business data privacy, security and compliance
- OpenAI: enterprise privacy commitments
- Anthropic: data ownership and management for Claude for Work
Checked 9 October 2026. AI product controls and data terms change frequently. Businesses should verify the current terms and administrator settings of every tool they approve.
Robius.news | Dubai, UAE | 2026 | Built to be first. Built to be trusted.