
A text message asking for your banking OTP used to feel normal because banks themselves trained customers to expect one. That pattern is changing in the UAE.
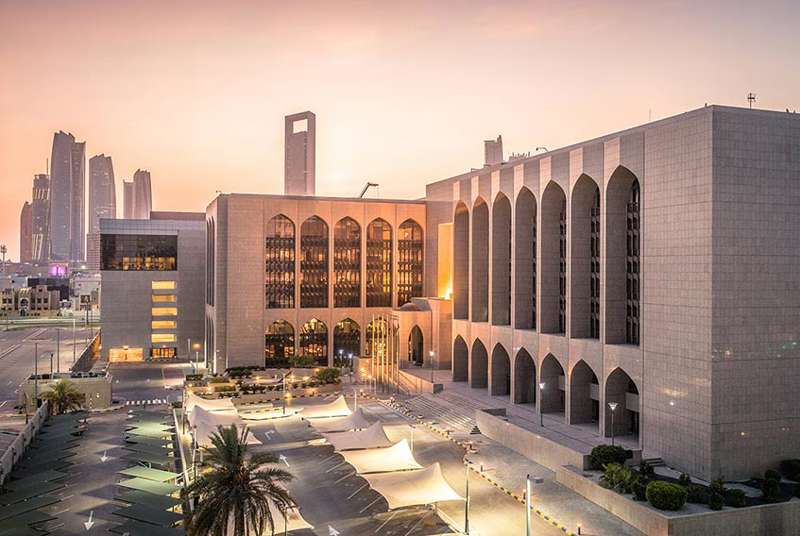
UAE banks have been moving toward in-app approvals, biometric checks and stronger multi-factor authentication. The Central Bank of the UAE said in its 2025 annual report that financial institutions were required to adopt stronger authentication controls with reduced reliance on single-factor mechanisms such as SMS OTP.
As UAE banks reduce reliance on SMS OTPs, fraud attempts can shift toward convincing customers to approve in-app or biometric authentication requests.
Anyone using UAE mobile banking, payment cards or digital wallets, especially customers who receive unexpected authentication prompts or bank impersonation calls.
In-app approval and biometrics can reduce dependence on text-message codes that can be intercepted, phished or read aloud to fraudsters.
Stronger authentication does not stop social engineering if a customer is persuaded to approve a fraudulent payment or login in the bank app.
UAE financial institutions are expected to continue strengthening multi-factor authentication and fraud controls as digital payments expand.
Never approve an authentication request you did not initiate; end unexpected calls and contact the bank through its official app, card or verified website.
Customers benefit from stronger authentication, while scammers benefit when they can socially engineer a genuine customer into approving the action themselves.
Authentication methods differ by bank and transaction type; customers should follow only prompts tied to actions they personally initiated.
Watch your own bank's authentication changes and any new fraud warnings involving app approvals, biometrics, beneficiary additions or device registrations.
For residents, that creates a practical anti-fraud rule: if someone calls, texts or messages you and asks you to read out an OTP, approve a banking notification or authenticate an action you did not start, the problem is not which channel the code arrived through. The problem is that somebody else is trying to make you authorise their transaction.
SMS Is Not Disappearing From Banking
This is where the headline needs precision. SMS itself has not vanished from UAE financial services. Banks and exchange businesses can still use text messages for notifications and other customer communications.
The security shift is about authentication: moving sensitive approvals away from dependence on a code sent through a separate message and toward stronger combinations of possession, biometrics, secure app prompts and other factors.
The CBUAE’s current Open Finance rules, for example, require reliable authentication and at least two factors drawn from knowledge, possession or inherence when users access information or initiate transactions through covered providers.
An App Approval Can Still Be Socially Engineered
Replacing an OTP with a push notification removes one common attack path. It does not make the human part of fraud disappear.
A scammer can still call while a fraudulent transaction is waiting for approval and tell the victim to open the bank app, use Face ID or fingerprint authentication and press “approve.” If the victim believes the caller is from the bank, the stronger technology can still be used to authorise the wrong action.
The safety question is therefore simple: did you initiate the action you are being asked to approve? If not, do not authenticate it.
The New Red Flags
- Someone contacts you first and says an urgent bank action needs your approval.
- You receive an in-app authentication request for a payment, beneficiary or login you did not start.
- A caller tells you to approve a notification “to cancel” or “reverse” a transaction.
- You are asked to share an OTP, PIN, password or authentication code over the phone or chat.
- You are pushed to act immediately because your account will supposedly be blocked, frozen or charged.
Why Fraudsters Like Urgency
Authentication systems are designed to prove that the person using the registered device or credential is authorising something. Scammers try to bypass that control psychologically rather than technically: they convince the genuine customer to complete the authentication for them.
That is why a message can look convincing and still be fraudulent. The logo, sender name or correct final digits of an account do not change the underlying rule. A legitimate-looking prompt is only safe when it corresponds to an action you knowingly started.
What to Do Instead
- Do not approve unexpected app prompts or biometric requests.
- Do not read an OTP or security code to a caller.
- End the call and contact the bank through the number inside its official app, on your card or on its verified website.
- If you already approved something suspicious, contact the bank immediately and report the transaction through its fraud channel.
- Review recent beneficiaries, cards and login activity if your bank provides those controls.
Sources
- Central Bank of the UAE, Annual Report 2025: stronger authentication controls and reduced reliance on single-factor mechanisms such as SMS OTP — CBUAE
- CBUAE Rulebook: current authentication requirements for Open Finance services — Article 18: Authentication
- Gulf News, 17 September 2026: current UAE banking implementation of in-app and biometric payment verification — Gulf News
Checked 17 September 2026. Bank authentication methods differ by institution and transaction type.
Robius.news — Dubai, UAE — 2026 | Built to be first. Built to be trusted.